
Bridge the Gap Between Security and Strategy
Transforming cybersecurity from a technical roadblock into a strategic business enabler.
We help organizations reduce breach costs, improve efficiency, and meet regulatory expectations without unnecessary complexity
Secure. Compliant. Resilient.
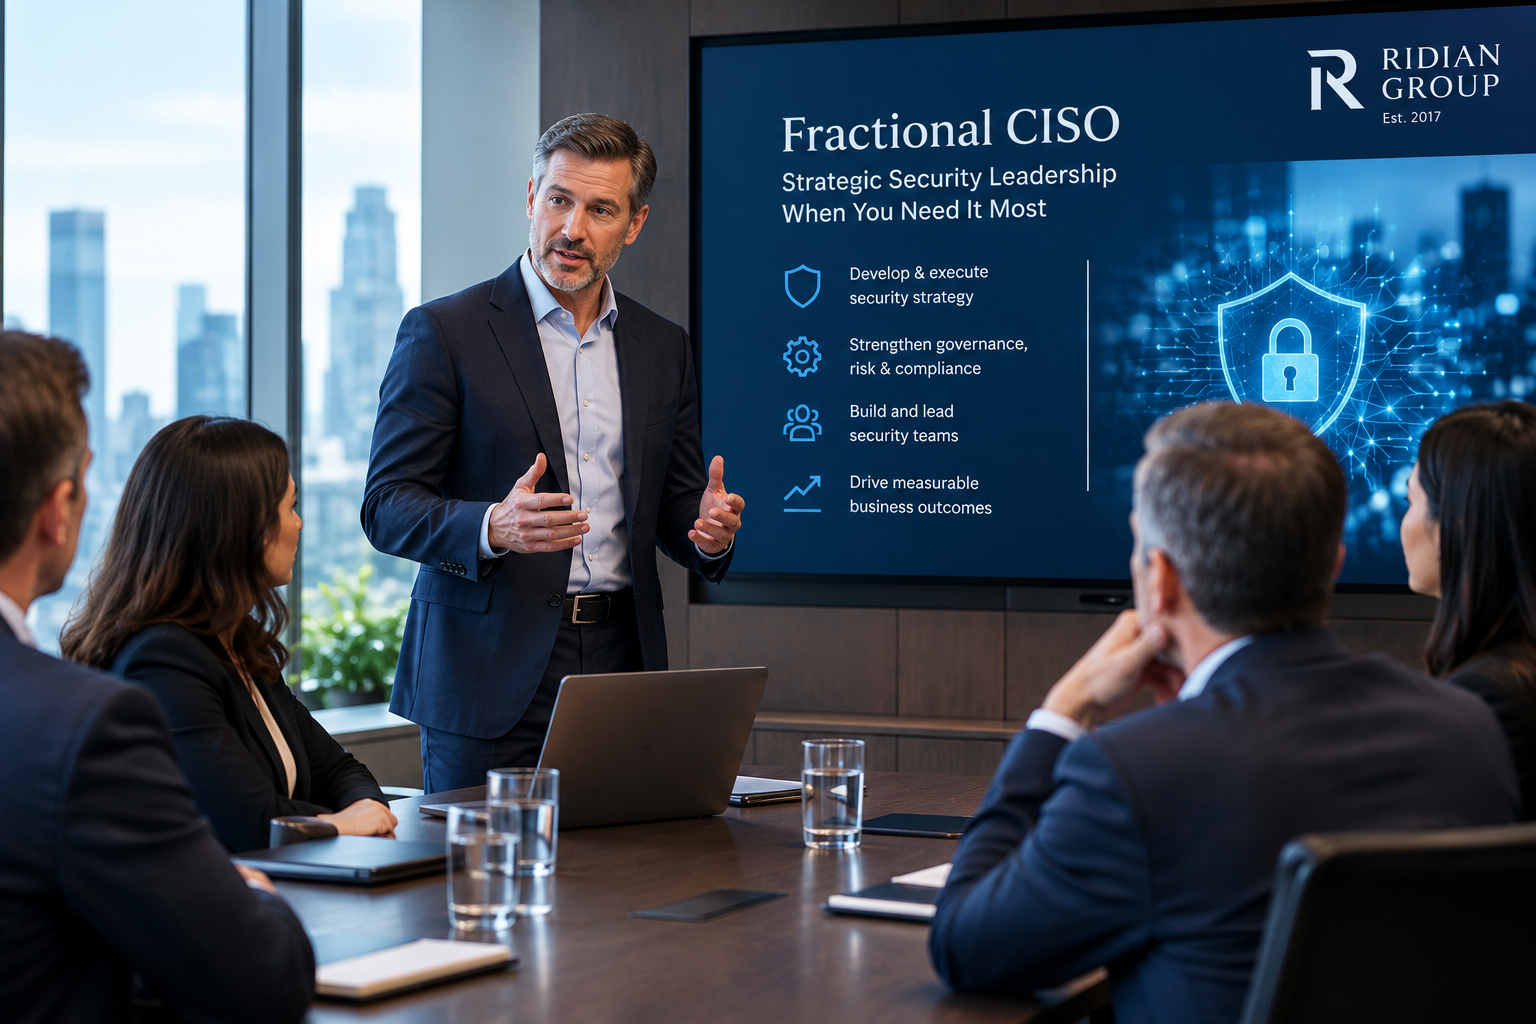
Fractional CISO / vCISO
Strategic advisory for executives and boards, vulnerability assessments, and cybersecurity roadmaps tailored to legal expectations and market entry strategies
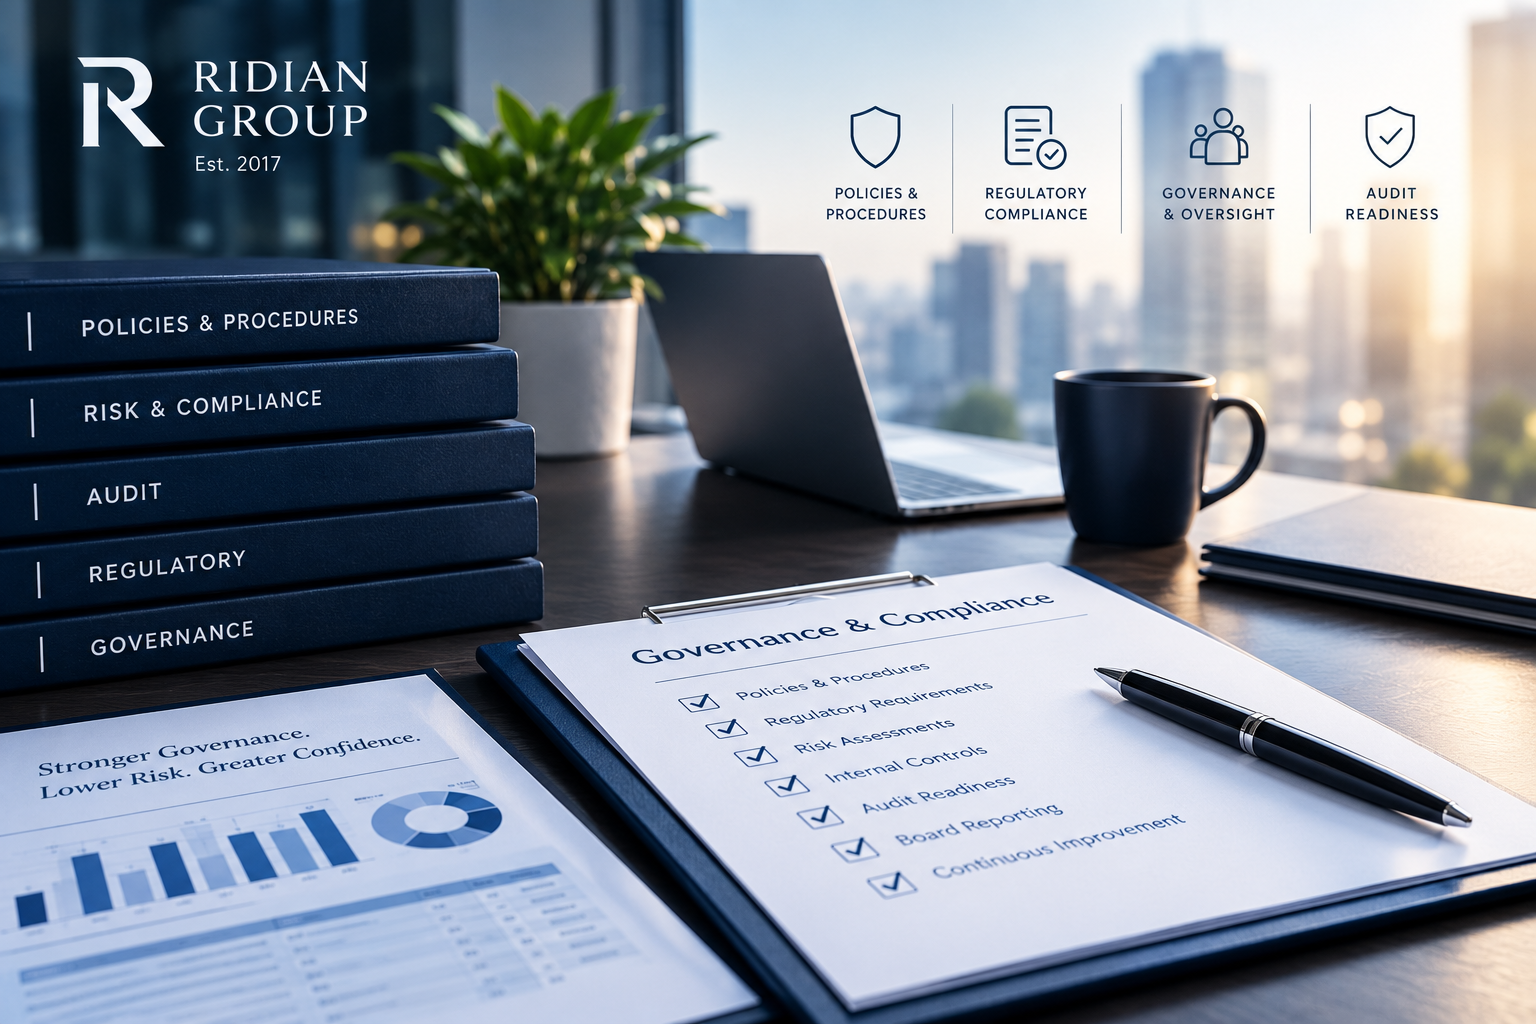
Governance & Compliance
Regulatory alignment, in-depth SOC 2 reviews, vendor risk assessments, and strict adherence to the NIST Cybersecurity Framework
Program Management
Transform security requirements into fully operational enterprise programs. Establish secure architectures, policies, and incident response processes while integrating vulnerability management and business continuity into a unified framework
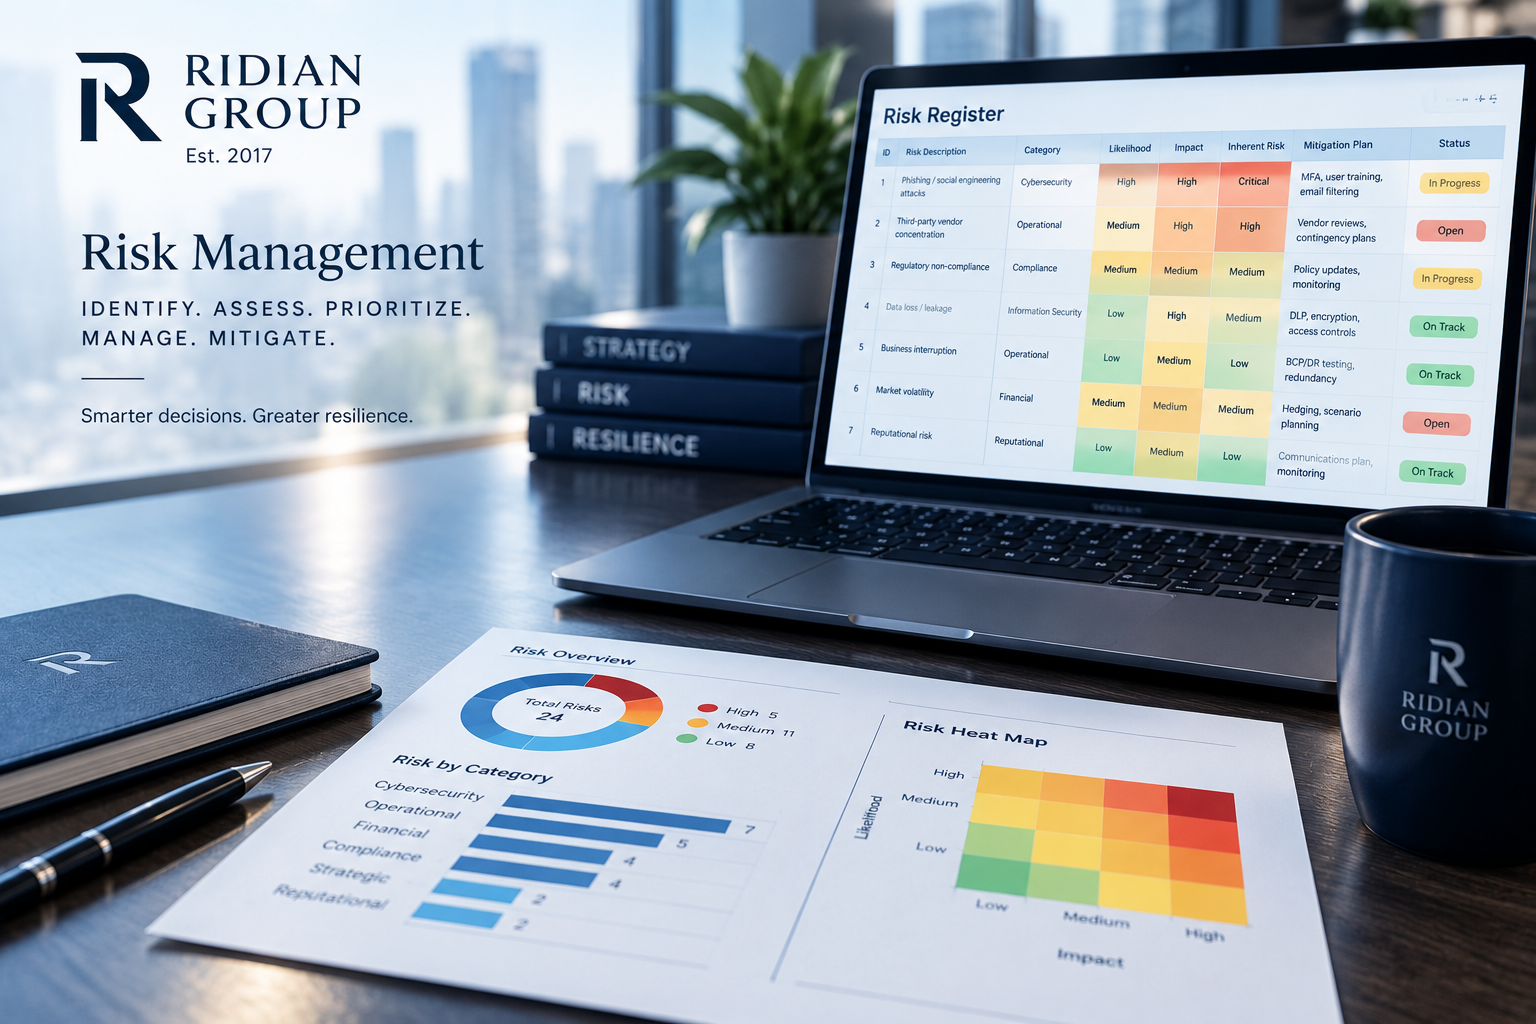
Risk Management
Build a practical risk management framework that identifies, prioritizes, and communicates the risks that matter most to your organization. We help leadership establish risk registers, KRIs, risk reporting, and effective mitigation strategies
Cybersecurity & Technology Executive Search
Identifying and recruiting high-impact cybersecurity and technology leaders across Information Security, Governance, Risk & Compliance (GRC), Program Management, and Infrastructure